The IHI Group has established the IHI Group Information Security Policy to protect important information assets, including corporate management and technical information, as well as the confidential information of customers and business partners. The policy also aims to ensure that, even in the event of an information security incident, the Group can respond promptly and appropriately to minimize damage.
Under this policy, the Group has established measures and frameworks to maintain and improve information security.
Policy
IHI Group Information Security Policy
The IHI Group hereby sets the following IHI Group Information Security Policy for the purpose of ensuring the security of information assets in its possession and thereby further solidifying its trust-based relationship with customers, users and society.
(Basic Activities)
The IHI Group will take appropriate measures with technology, organization and employees, in order to protect information assets against any leakage, theft, loss, destruction, illegal access, and disaster.
In the event of any security problem regarding this information, the IHI Group will locate the cause as quickly as possible, and exert every possible effort to minimize the damage incurred.
(Information Assets)
“Information assets” refer to the information the IHI Group handles in the course of business activities, regardless of the type of media, and the equipment, facilities and services necessary for handling such information.
(Scope)
This Information Security Policy applies to all those using the information assets of the IHI Group, including but not limited to officers and employees of the IHI Group companies and temporary staff.
(Compliance with Laws, Regulations, etc.)
The IHI Group will strictly observe the laws, regulations and codes pertaining to the protection of information assets, and the requirements and obligations regarding information security provided for in the agreements with the customers.
(Education)
The IHI Group companies will provide all those using the information assets of the IHI Group with the necessary education on information security to enhance and maintain their awareness thereof.
(Management of Information Security)
The IHI Group companies will establish a mechanism of implementing and managing information security by taking measures such as establishing rules concerning information security and appointing persons in charge of information management, thereby conducting, maintaining and improving information security activities on a continual basis.
(Responsibilities of Senior Management)
The Senior Management of the IHI Group will set the example of enforcing this Information Security Policy. In the event of any infringement of this Policy, senior management will address the situation properly by defining their authorities and responsibilities, and do their utmost to resolve the problems, diagnose their causes, and prevent their recurrence.
(Punishment)
Any action in violation of the rules of information security will incur punishment according to the employment regulations of IHI Group companies.
(Announcement)
This Information Security Policy will be announced and notified to all those using the information assets of the IHI Group as well as being announced to the public.
Governance
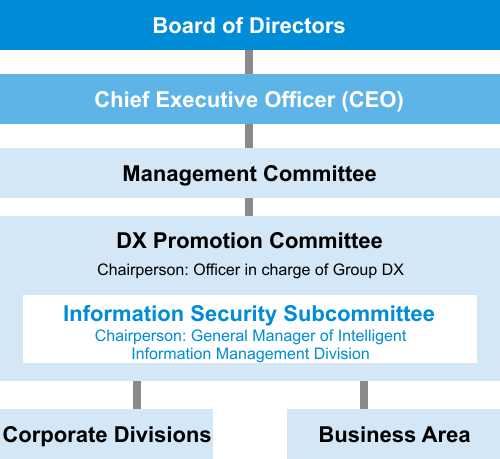
The IHI Group has established an Information Security Promotion Framework, chaired by the Officer in charge of Group DX as its Chief Information Security Officer. The Information Security Subcommittee operates within the DX Promotion Committee as an organization in charge of promoting the company’s information security activities overall. An Information Security General Manager is appointed at each IHI corporate division, Business area, Business Unit, and affiliated company to accelerate activities under this framework. Matters of particular importance regarding operation and management are discussed by the Board of Directors.
Information Security Promotion Framework
Information Security Subcommittee
Chairperson
General Manager of Intelligent Information Management Division
Subcommittee members
Business areas, Business Units, and corporate divisions
Secretariat
Information Security Department
Number of meetings convened in FY2025
3
Risk Management
Information Security Management System
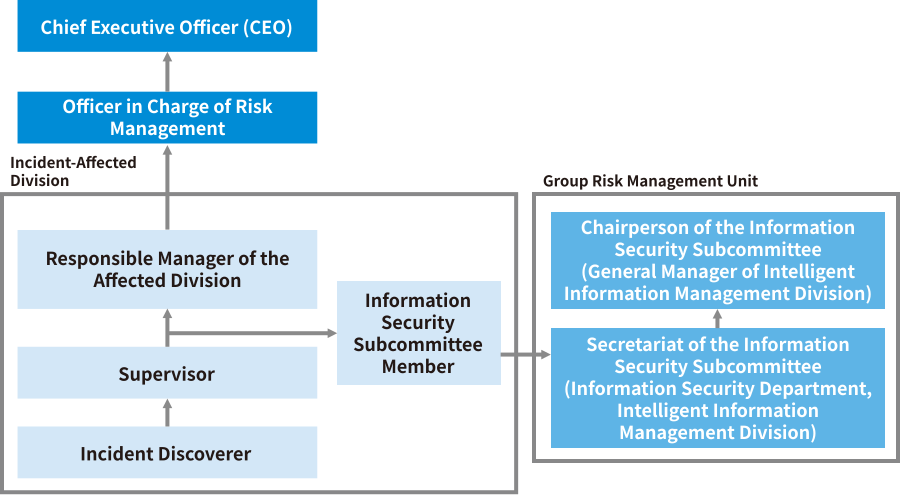
The IHI Group has established a Group-wide information security promotion system, and is prepared to respond quickly under this framework in the event of an information security incident or accident, including a cyber attack. If employees identify an actual or potential information security incident or accident, they escalate the matter to the information security personnel at both the divisional and corporate levels in accordance with the escalation route for incident report established by each division, enabling an organization-wide response.
The Information Security Subcommittee, consisting of IHI’s corporate divisions, business areas, and Business Units, meets three times a year as a council for promoting information security measures, and plans, implements, and checks information security measures on an annual cycle. Taking into account the internal and external environment, such as an increase in telecommuting and the growing threat of cyber attacks, key measures were set for each fiscal year and implement measures accordingly. In addition, each organization evaluates security risks based on the information assets and business processes they handle, and reflects these in their own organization’s countermeasure plans.
Since fiscal 2019, the Group built a three-stage auditing framework for information security consisting of three types of audits by its own organizations, corporate divisions, and Internal Audit Division from different auditors to strengthen checks (“C”) in the PDCA cycle. Each organization (IHI divisions and affiliated companies) conducts its own internal audit, the corporate division executes documentation audits and on-site audits, and Internal Audit Division implements audits.
Divisions and affiliated companies involved in highly sensitive national projects in the IHI Group must undergo annual reviews by an external specialized agency to renew the ISO 27001 international information security certification for maintaining a high level of security.
Escalation Route for Incident Report
Establishing the SOC and CSIRT
In order to respond to the growing threat of cyber attacks, the IHI Group has set up a SOC (Security Operation Center) and conducts security monitoring of PCs, servers, and network equipment. Additionally, the Group has established a CSIRT (Computer Security Incident Response Team) and put a framework into place for quickly responding to incidents detected through security monitoring. The Group has also prepared a response procedure manual for ensuring its ability to appropriately respond to cyber security incidents, outlining response procedures such as identifying the scope of breach and taking containment measures. Furthermore, response training assuming a cyber security incident is conducted at least once a year and appropriateness of the procedures is assessed.
Measures to Prevent Information Leakage During Remote Work
Remote work, introduced as a measure to prevent the spread of the COVID-19 throughout the IHI Group, has gained traction as one of many work styles. However, remote work increases information security risks such as improper use, loss, or theft of information devices due to the higher number of information devices taken outside of the office.
To prevent the improper use of information devices, the IHI Group works to raise employee awareness through e-learning and internal newsletters covering security compliance rules for work done outside the office. These rules specifically prohibit personal use of company computers and prohibit business data from being stored on personal IT devices of the individual and/or family.
In addition, as a general rule when performing work outside of the company, the Group has implemented measures to make use of computers that do not store business data, reducing information leakage upon loss or theft of these devices.
Information Security Measures
The IHI Group takes steps to address information security risks from three perspectives: rules, tools, and education.
The rules include the IHI Group Information Security Policy, IHI Group Information Security Measure Standards, and Information System User Rules. The Group has adopted antivirus software and other security tools, which are always kept up to date. The services of specialized security firms are being used to investigate public servers, and any vulnerabilities found are fixed.
Evaluation of Information Security Measures
The IHI Group assesses the information security measures of the entire Group quantitatively every year based on the benchmark for information security measures implemented by companies offered by the Innovation Platform Agency, Japan (IPA).
The target score for information security measures is 4 out of 5, and the Group achieved a score of 4.0 in fiscal 2025. In fiscal 2026, the IHI Group will continue its efforts to enhance its overall level of information security.
Employee Education
E-learning Related to Information Security
The IHI Group provides e-learning related to information security on a yearly basis, targeting all employees. By deepening their understanding of information security rules and tools, the Group aims to maintain and raise employee information security awareness across the IHI Group. The training content is continuously reviewed in light of internal and external trends to ensure that employees can appropriately respond to the latest threats.
E-learning Related to Generative AI
In response to the rapid advancement of generative AI in recent years, the IHI Group has implemented e-learning related to generative AI to all employees beginning in fiscal 2025. This initiative is designed to strengthen employees’ understanding of core principles, promote responsible and effective use, and highlight practical applications across the business. The program also addressed threats specific to generative AI, with the objective of ensuring that employees are equipped with the knowledge and awareness necessary to leverage these technologies safely and appropriately.
Metrics and Targets
Evaluation of Information Security Measures
Item
Scope
Unit
FY2022
FY2023
FY2024
FY2025
Evaluation (out of 5)
IHI and consolidated subsidiaries
Score
3.7
3.8
3.8
4.0
Rate of Participation in e-Learning Related to Information Security
Item
Scope
Unit
FY2022
FY2023
FY2024
FY2025
Participation rate
IHI
%
96.9
98.9
99.1
99.2
Rate of Participation in e-Learning Related to Generative AI